The Three Pillars of Trust for AI in Software Development
Here's the truth about AI agents in software development today: everyone's beginning to use them, but few really trust them.
For platform teams, this trust gap is both a challenge and an opportunity. Developers need a few things before they rely on AI agents for important work, and platform teams are in the best position to provide them. This post explains what those things are, and how to build them.
The Trust Paradox in AI-assisted Software Development
According to the 2024 Stack Overflow Developer Survey, 62% of developers use AI tools, up from 44% the year before, but their favorable view of those tools dropped from 77% to 72%. Usage is climbing while confidence is declining.
The reason is that most AI tools create a "trust but verify" problem that doesn't scale. They generate code that looks right, and leave all the validation to you: whether it works, whether it handles edge cases, and whether it breaks against real production constraints. Every time you find an issue during manual testing, you trust the agent a little less.
Meanwhile, the conversation is about which model to use and how to write the perfect prompt. Almost nobody is talking about giving AI agents the production-like environments they need to produce real results.
Why Current AI Tools Aren't Meeting Developers' Needs
The Code Suggestion Trap
Most AI tools today are advanced autocomplete. They produce code snippets, maybe entire functions, and leave you to figure out the rest. Does the code work? Has it been tested? Is it secure? You can spend as much time checking the agent's homework as you saved by using it.
The promise was more productivity. The reality is more validation.
The Local Development Wall
An AI agent running on a laptop doesn't know about your internal APIs, your database schemas, your microservices, or the network policies that make your application work. It generates code that looks fine locally and fails the moment it meets your real infrastructure, because it had to make assumptions about your application that aren't true.
The Security and Governance Gap
How do you audit what an AI agent did? How do you make sure it doesn't expose sensitive data or break compliance requirements? When developers install AI tools on their laptops, there's no visibility into what the agent accessed, what it did, or whether it followed your security policies. For regulated industries, that alone rules out AI adoption.
The Platform Engineering Opportunity
Developers are experimenting with AI on their own, because nobody has given them a better option. It's the same pattern we saw with cloud adoption: when platform teams don't provide a path, developers make their own. With AI agents the stakes are higher, because internal code and secrets can end up with external model providers.
Right now, every developer runs their own AI setup, with no governance, no observability, and no standardization. That's a problem platform teams know how to solve: build a golden path that's better than the alternatives, and developers will take it.
Three Pillars of Trustworthy AI in Software Development
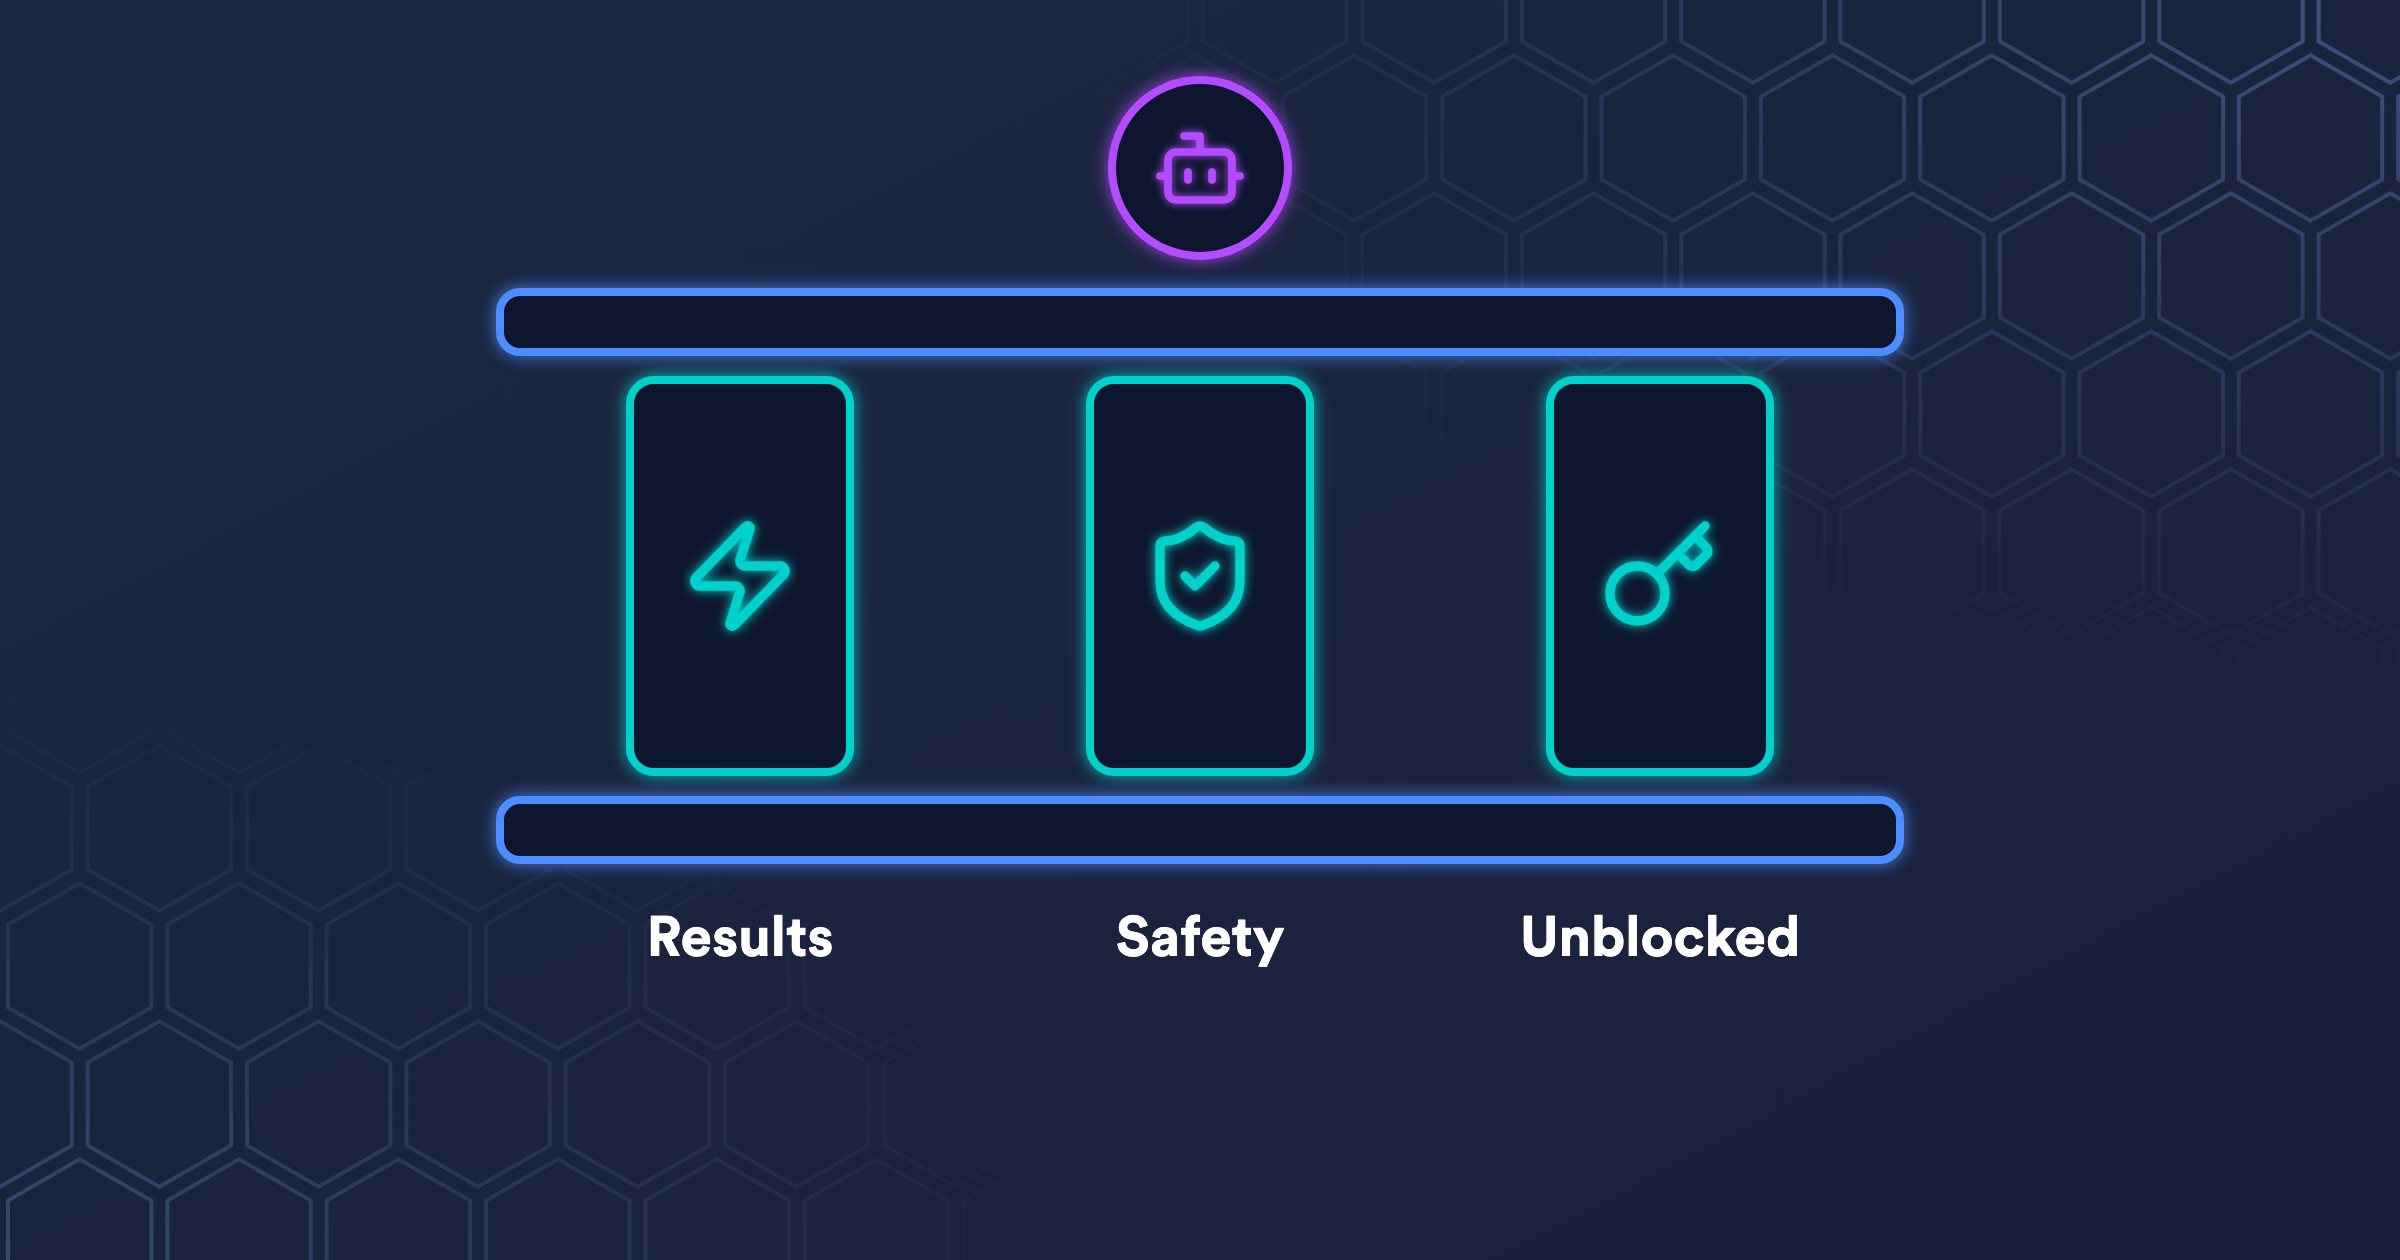
What developers need to trust AI agents comes down to three things.
Results ("I describe what I want, and it actually happens")
Developers need agents that take a request like "add authentication to this API" and deliver a working feature: not code that might work, but a deployed endpoint, connected to a real database, that you can test right away.
That requires access to your actual application. When an agent can run the application with its real services, APIs, and data, it stops guessing and starts verifying its own work against your actual constraints. Trust comes from seeing results: click a link, call an endpoint, see it working.
Safety ("I can experiment without breaking anything")
Safety means you can let an agent loose on a complex task without worrying that it takes down production, exposes sensitive data, or breaks your local setup.
That's where ephemeral environments come in. Every agent needs its own isolated application environment, created from the same definition as everyone else's, with no configuration drift, no state left over from previous runs, and no way to step on another developer's or agent's work. The agent itself runs in a light sandbox with only the access it needs, separate from the application it changes. Governance, security policies, and access controls are built into both, so the agent works within the same boundaries you'd set for a new team member, with monitoring and a full audit trail.
Unblocked ("I don't have to configure anything")
Developers shouldn't have to become infrastructure experts to try an AI workflow. Setup, configuration, and troubleshooting kill experimentation before it starts. When trying something new is easy, developers try it; when it's complicated, they stick with what they know.
When the platform takes care of the environments, developers stop thinking about infrastructure and start thinking about the problem they want to solve.
The Missing Piece: Infrastructure
Trust in agentic development needs three things working together: capable models, good prompts, and the right infrastructure. Most teams have figured out the first two. The third one, a production-like context for the agent to work in, is what makes realistic output possible.
Modern applications are code plus configuration, secrets, infrastructure, network policies, deployment workflows, monitoring, and logging. An agent that works within that full context produces different output: an API that integrates with your auth service, follows your database conventions, and deploys the way your application deploys. And because the agent tests its change in an environment that mirrors production, when it says "this works," you can believe it.
That puts platform teams at the center of AI adoption. Developers get environments that just work, and the platform team makes sure security policies, compliance requirements, and operational standards are enforced in every one of them. Instead of guessing what developers are doing with AI, you get observability, governance, and standardization. And as more developers see agents deliver working results, adoption spreads on its own.
Single agents are only the beginning. As teams run many agents in parallel on bigger workflows, the same patterns (an isolated environment per agent, policy enforcement, observability) are what make it possible at scale. For how to run coding agents on Kubernetes with this architecture, read Why Run AI Coding Agents on Kubernetes? and How to Run AI Coding Agents on Kubernetes.
The Bottom Line
Great models and prompts get you started, but developers trust AI agents when they see them deliver working results, safely, without setup. That depends on the infrastructure platform teams build, and the teams that build it first will lead their organization's adoption of AI.